When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works .
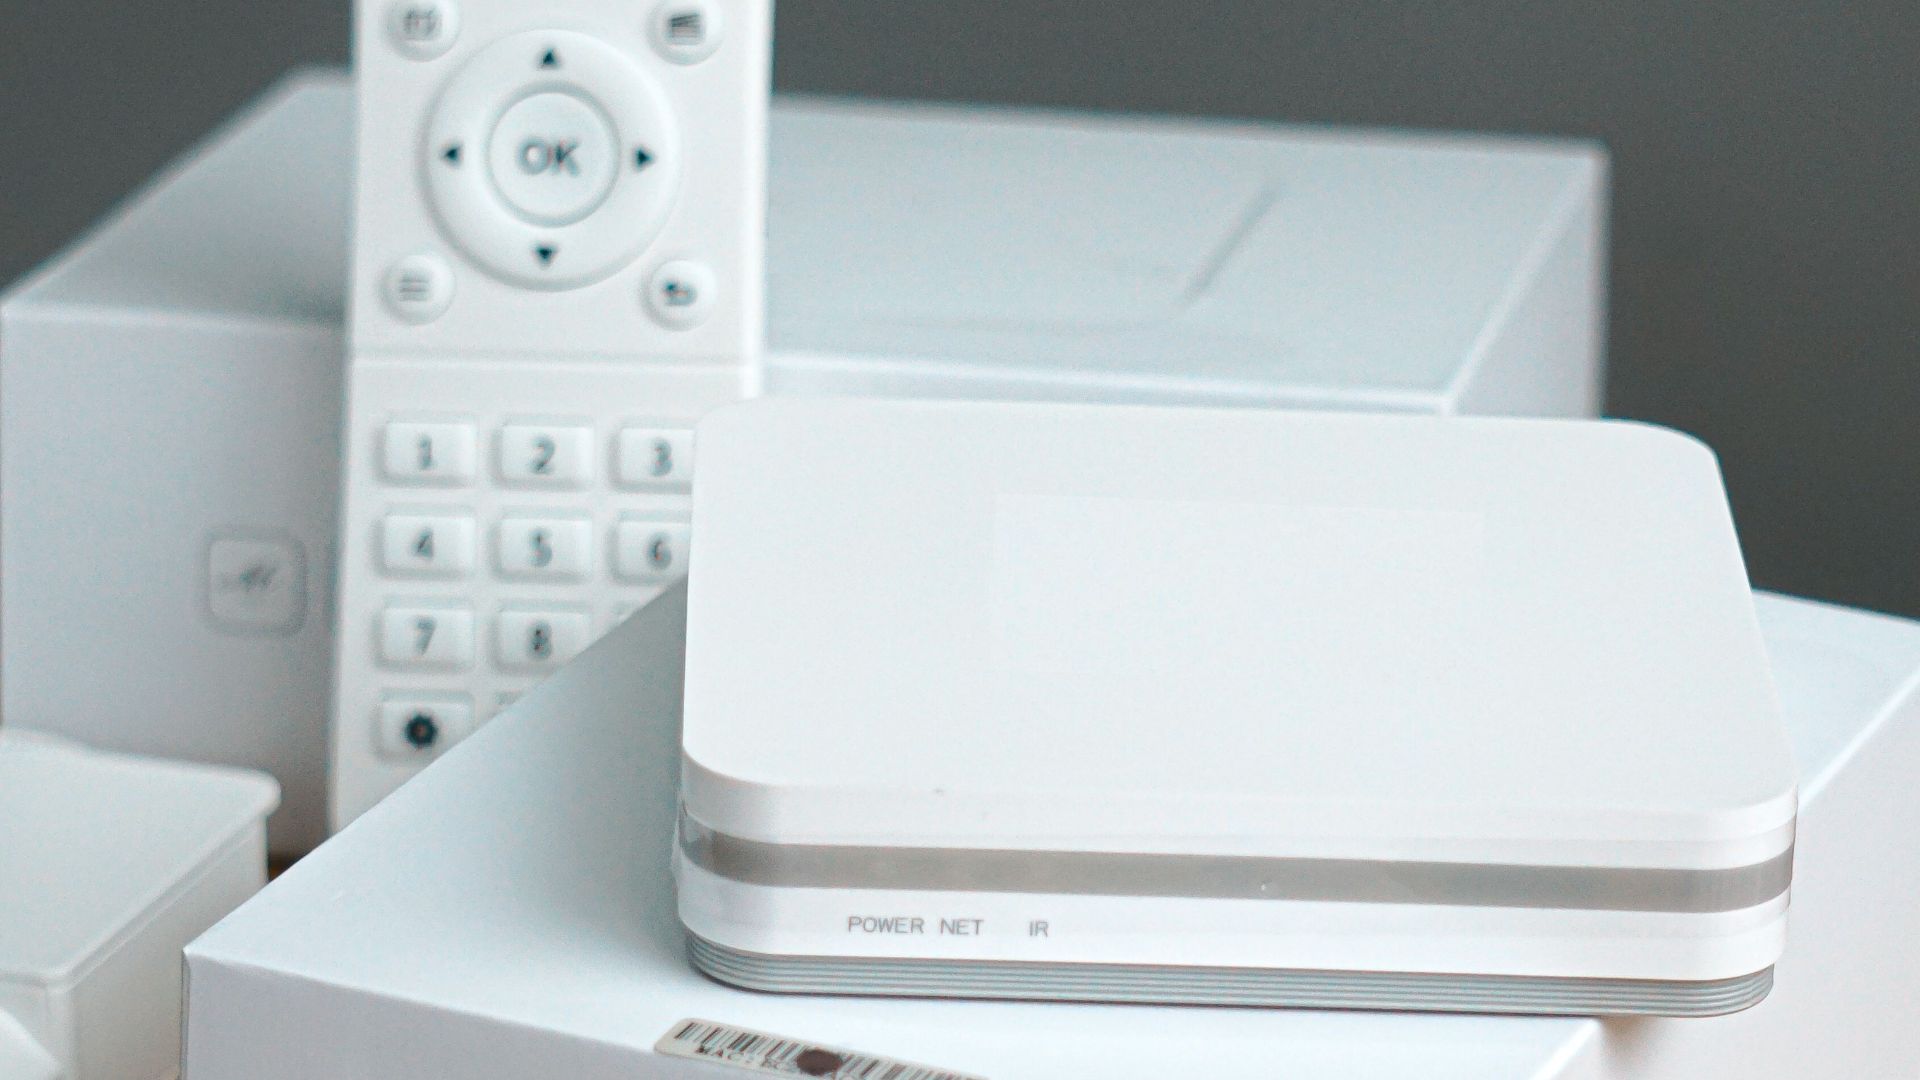
“Videostrong monetized the backdoor by selling access to criminal affiliates and loading those affiliates’ malware modules onto infected devices,” the company said in the Google Cloud blog post. It also added, “We found this malicious software built directly into many different device models and brands over multiple years, supported by dedicated infrastructure and constantly evolving configurations to evade detection and manage their affiliates. We believe this campaign wasn’t an isolated rogue insider or a development oversight. As a result, Google has cut ties with Videostrong and banned them from making devices with preloaded Google apps.”
There have been supply chain attacks in the past, wherein a third-party compromises a trusted product to steal data, like some Ledger hardware wallets that have been sold by a reseller in Southeast Asia and Europe . Although Google did not characterize this as a supply chain attack, as it was perpetrated by the manufacturer itself and not a third-party operator, it still compromised a supposedly trusted operating system, leading to millions of victims. This incident also shows how even the simplest of devices can be used to execute complicated attacks, like how a Chinese couple hid a PC behind a fridge in a Japanese hotel and targeted 2.4 million victims.
Follow Tom's Hardware on Google News , or add us as a preferred source , to get our latest news, analysis, & reviews in your feeds.
Security researchers find surveillance implants in Chinese-made routers sold worldwide
Geekom admits to shipping malware-laced network drivers for AMD mini PCs
Key considerations
- Investor positioning can change fast
- Volatility remains possible near catalysts
- Macro rates and liquidity can dominate flows
Reference reading
- https://www.tomshardware.com/tech-industry/cyber-security/SPONSORED_LINK_URL
- https://www.tomshardware.com/tech-industry/cyber-security/certified-android-tv-manufacturer-put-unauthorized-backdoor-in-set-top-boxes-google-reveals-oem-sold-access-to-criminal-affiliates-for-1-3-million-devices-used-massive-network-as-botnet-for-ad-fraud-residential-proxy#main
- https://www.tomshardware.com/membership
- Creator says Amazon closed his account after he tried to buy seven Nvidia DGX Sparks
- Chinese survey ship loitering near undersea cable ignores Philippine demands to withdraw
- Certified Android TV manufacturer put unauthorized backdoor in 1.3 million set-top boxes, Google reveals
- Steam Survey shockwaves felt as proportion of 32GB RAM systems drops by more than 5%
- How Companies Are Using NVIDIA DSX to Break the Power Bottleneck
Informational only. No financial advice. Do your own research.