When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works .
The malware’s payload consists of XMRig and Iron miners, connected to Kryptex mining infrastructure, with infected servers becoming scanners and exploit servers. The “primary commonality amongst the first 900 victims” was contact with “an endpoint for the Russian crypto mining service,” Lumen says. This indicates that it may be financially motivated. “AI infrastructure is becoming an attractive target” because exposed AI services may contain valuable data and hardware access, especially GPUs . In the meantime, it has “blocked all traffic to and from the PoeLLM C2 servers.”
The primary targets are LiteLLM, a proxy server (AI Gateway) to call LLM APIs, a way companies can route their apps to many models through one endpoint, and Gotenberg, a Docker-based API for PDF conversion, which has a guide warning not to expose it to the internet. Also hit are Ollama, which allows you to run open-weight models on your own hardware, although it is not internet-exposed by default, and Gitea, a self-hosted Git platform. Ivanti Sentry, an enterprise gateway appliance, “may also have been targeted,” and one instance was how Lumen discovered the campaign.
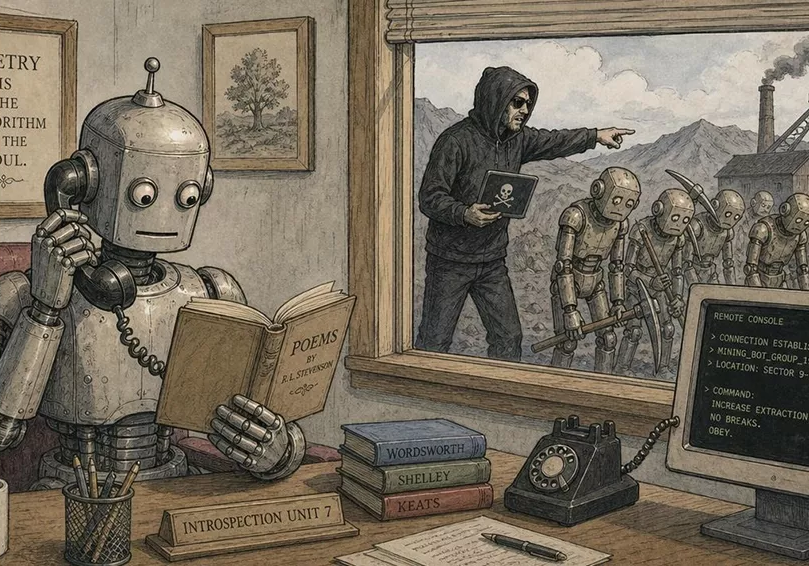
Although the malware’s methodology involves leveraging poetry, this is only for pointing the infected servers to the C2 server. It is not a form of an AI jailbreak through harmful requests or prompt injection , or what is known as “adversarial poetry,” described in a paper last year.
The poem, “On the Nature of Connection,” was first committed in April, with each new version pointing to a new C2 server. The malware is able to decode the new address by pulling specific words and converting them into an IPv4 address. Lumen says that “the malware creator has not changed the pattern used in deciphering the poem” at the time of reporting. Using a poem likely aided in obfuscation as it is “a perfect vehicle for hiding an important message,” the researchers told The Register .
OpenAI's GPT-5.6 Sol and unreleased AI models break out of testing environment in 'unprecedented cybersecurity incident'
Geekom admits to shipping malware-laced network drivers for AMD mini PCs
Key considerations
- Investor positioning can change fast
- Volatility remains possible near catalysts
- Macro rates and liquidity can dominate flows
Reference reading
- https://www.tomshardware.com/tech-industry/cyber-security/SPONSORED_LINK_URL
- https://www.tomshardware.com/tech-industry/cyber-security/cryptomining-malware-used-poetry-to-infect-more-than-3-400-servers-researchers-say-four-words-in-the-poellm-verse-changed-11-times-point-the-botnet-to-new-servers#main
- https://www.tomshardware.com/membership
- We tested gaming performance in 17-year-old Windows 7 on a modern gaming PC against Windows 11
- Into the Omniverse: How Developers Turn Ideas Into Simulations With Frontier AI Agents
- Mistral’s new Large 4 trails some Chinese open models in independent tests
- Sandisk NAS 800 1.92TB SSD Review: Endurance at a premium
- PC shipments tumble over 20% in 3Q26 as chip shortages bite
Informational only. No financial advice. Do your own research.