When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works .
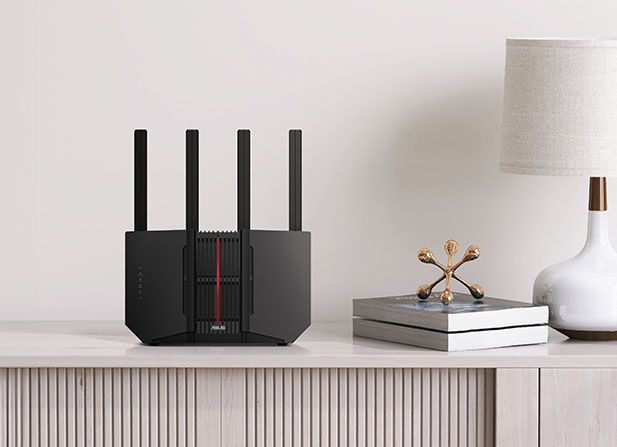
Asus recommends that users “only import VPN client configuration files from trusted sources.” The two CVEs, CVE-2026-14157 and CVE-2026-13313, score 9.4 and 8.9 out of 10 on the Common Vulnerability Scoring System (CVSS) 4.0 scale, which measures vulnerability severity. Asus names firmware series rather than models: 3.0.0.6_102 for both bugs, with the 3.0.0.4_386 and 3.0.0.4_388 series also affected by the Telnet one.
The routers can act as a VPN client when set up with a configuration file from a VPN provider. Things go wrong when crafted text inside the uploaded files is read as formatting instructions rather than plain data. VPNs are commonly used to bypass filters and access otherwise unreachable content, but the risk here applies to owners who import VPN configuration files into the router itself, not to VPN apps on a laptop or phone.
The separate Telnet flaw relies on enabling the service first before running commands that could impact the network. Besides the firmware update, Asus recommends a strong, unique admin password with “at least 10 characters, with a mix of uppercase letters, numbers, and symbols.” To reduce risk in the meantime, Asus also advises against running “scripts, tools, or commands from untrusted sources on any device within your local network.” One risk is that “attackers may use social engineering to trick administrators,” the company says.
The VPN bug uses the same entry point as one disclosed by VulnCheck in 2024, CVE-2024-0401, which used a crafted OVPN profile. That makes Asus’s config file import, specifically through the web admin page, a recurring weak point. As a popular brand, Asus is also a likely target. The AyySSHush campaign utilized authentication bypasses, brute-force logins, and a command-injection flaw (CVE-2023-39780) to backdoor over 9,000 routers , as we reported at the time. The backdoor was even able to survive firmware updates.
Hidden backdoor found in Tenda routers lets attackers log in as admin without a password
Critical macOS Screen Sharing flaw gives attackers remote root access
Key considerations
- Investor positioning can change fast
- Volatility remains possible near catalysts
- Macro rates and liquidity can dominate flows
Reference reading
- https://www.tomshardware.com/tech-industry/cyber-security/SPONSORED_LINK_URL
- https://www.tomshardware.com/tech-industry/cyber-security/malicious-vpn-config-files-can-let-attackers-run-commands-on-asus-routers-companys-patch-also-fixes-a-bug-that-lets-a-logged-in-attacker-switch-on-telnet-with-root-access#main
- https://www.tomshardware.com/membership
- OpenAI says actors linked to China-based Moonshot AI spearheaded a campaign to extract its models’ hidden reasoning
- Grab a huge $520 saving on this RTX 5090 gaming laptop from MSI with 64GB DDR5 and a 2TB SSD
- Toshiba to double HDD production capacity amid devastating shortages
- From Training to Production, NVIDIA and CoreWeave Close the Loop on Agentic AI
- NVIDIA Opens Applications for 2027–2028 Graduate Fellowships With Awards Up to $60,000
Informational only. No financial advice. Do your own research.