Mark Tyson Social Links Navigation News Editor Mark Tyson is a news editor at Tom's Hardware. He enjoys covering the full breadth of PC tech; from business and semiconductor design to products approaching the edge of reason.
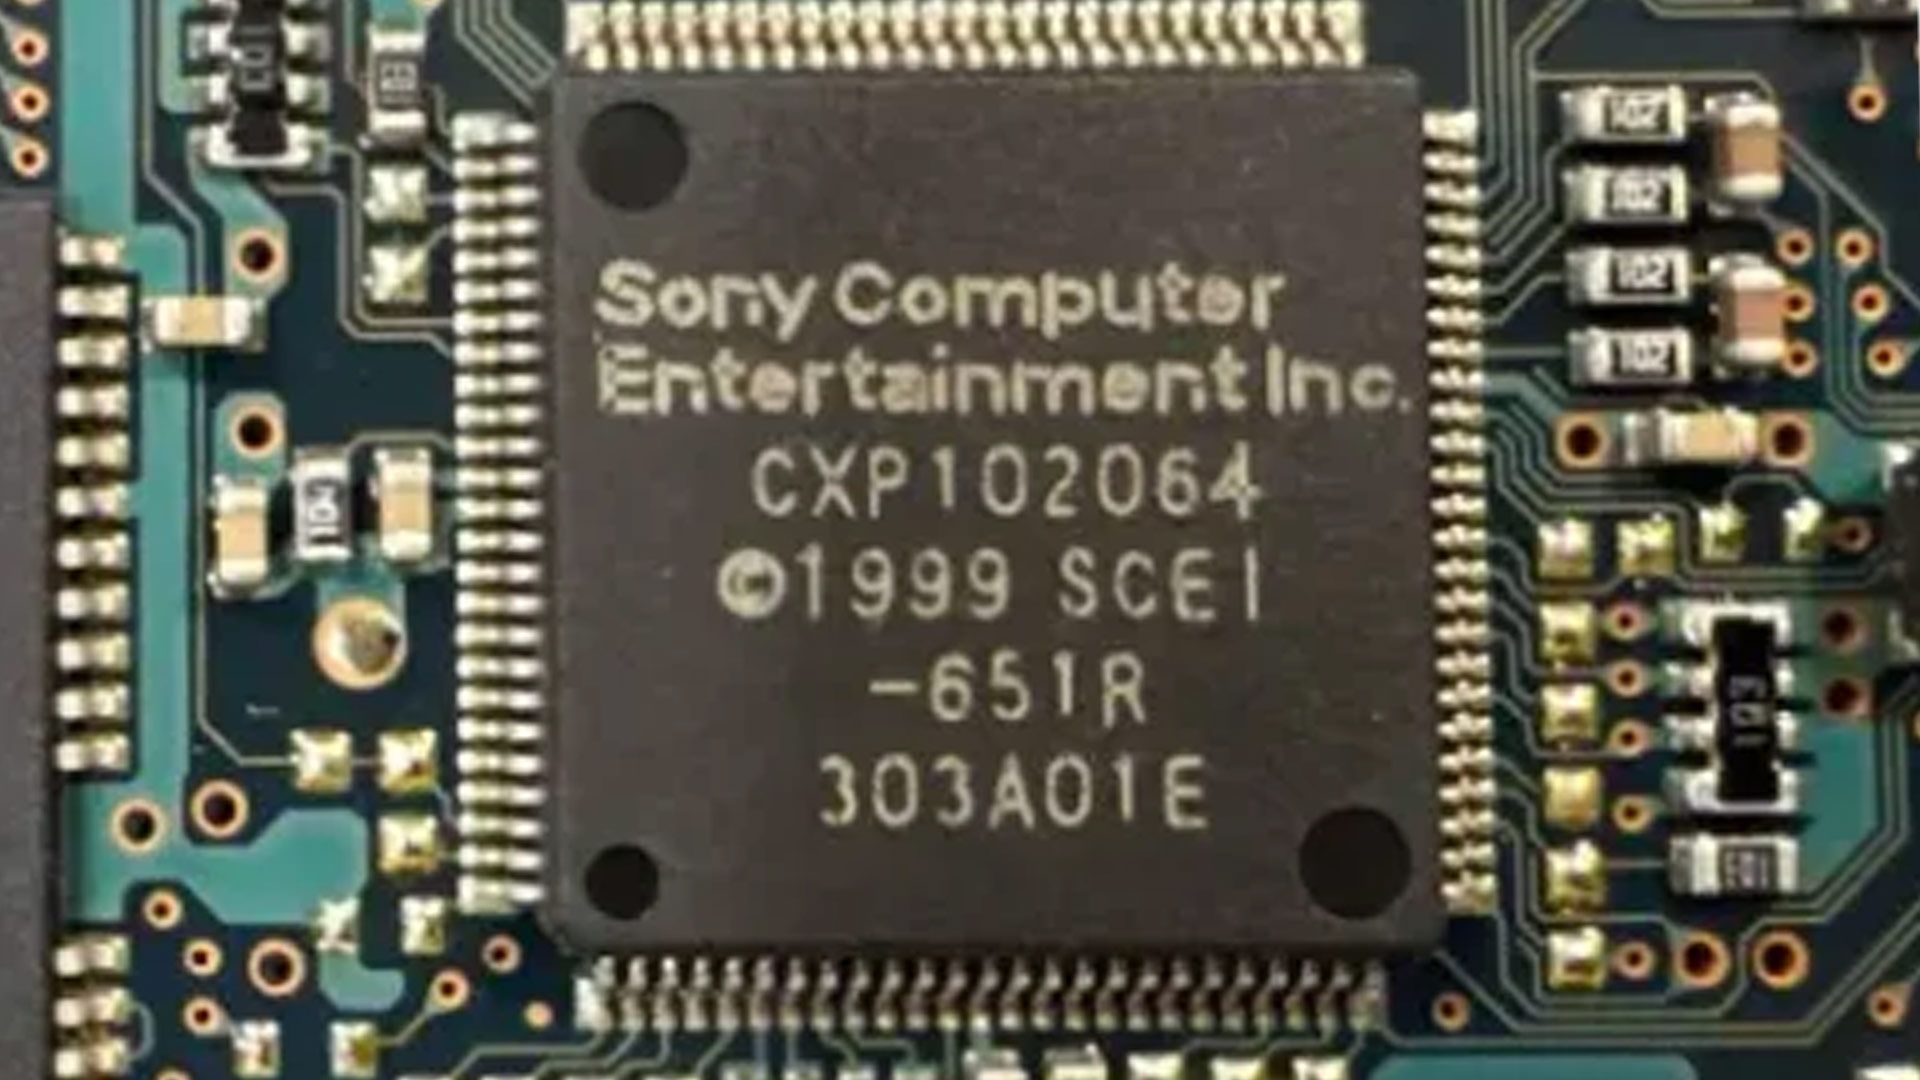
JeffreyP55 Admin said: The ‘magic security chip’ inside the original PlayStation 2 has been successfully reverse engineered and dumped after four years of effort. Original Sony PlayStation 2 security chip ‘broken wide open’ after 26 years — chemical decapping and four years of reverse engineering unlocks Mech… : Read more Too much time on my hands. Reply
uyjulian Hello! I'm one of the people involved in reverse engineering the MechaCon. Please take note of the following: * It is already possible to run backup/copied discs entirely using software methods (from memory card, HDD, or DVD video player exploit), and in the case of the 50k series and newer (Dragon MechaCon), can use the "force unlock" patch that does not require any patches to copied discs. * Most interesting information has been extracted from the PS3 PS2 emulator (ps2_emu) and the Dragon MechaCon already. * The dumps, alone, does not give enough information to create an """hardware""" ODE (optical drive emulator). However, it is possible to make a modchip that replaces the MechaCon, relying on the DSP to continue to read discs. * The current method to dump the ROM used in the SPC970 requires lots of writing to NVRAM using a specific command in an unintended way. This will reduce the lifetime of NVRAM, especially since it is lower capacity than NAND/NOR flash memory and does not have write leveling. * These dumps will eventually be useful for full-system low level emulation, as MagicGate and KELF/KIRX security goes through it. * These dumps are useful for vulnability searching, which can allow functionality to MechaPwn (code execution on MechaCon, unlocking security e.g. set disc type and max LBN) or TonyHax (unlocking PS1 mode to read any disc, on SPC970 based MechaCons and all PS1 MechaCons). * The contents of game discs (except those that use DNAS online authentication) are not encrypted. These dumps don't unlock anything additional there. * The functionality relating to "native" PS1 gaming on PS2 is related to IOP/EE, not MechaCon. Reply
Darkhands Fantastic work from you guys! Thanks for all that effort. Reply
Key considerations
- Investor positioning can change fast
- Volatility remains possible near catalysts
- Macro rates and liquidity can dominate flows
Reference reading
- https://www.tomshardware.com/video-games/playstation/SPONSORED_LINK_URL
- https://www.tomshardware.com/video-games/playstation/26-year-old-sony-ps2-security-chip-broken-wide-open-after-four-years-of-effort-reverse-engineering-enthusiast-successfully-unlocks-cxp102064-mechacon-chip#main
- https://www.tomshardware.com/membership
- NVIDIA Vera Rubin NVL72 Delivers Leading Performance in MLPerf Inference v6.1 Debut
- Get an AMD Ryzen 7 9800X3D for only $320 — 2-item Newegg combo saves $149 and nets one of the fastest gaming CPUs and a quality MSI X870E motherboard for only $
- AI Infra Summit: NVIDIA Vera Rubin and DSX Platform Advancements Showcase Energy Efficiencies of Optimizing Tokens Per Watt for AI Factories
- Perplexity Portable Computer Is Now Available on Windows, Powered by NVIDIA RTX
- ‘NBA 2K27’ With NVIDIA DLSS 5 Leads 28 New Games Coming to GeForce NOW
Informational only. No financial advice. Do your own research.