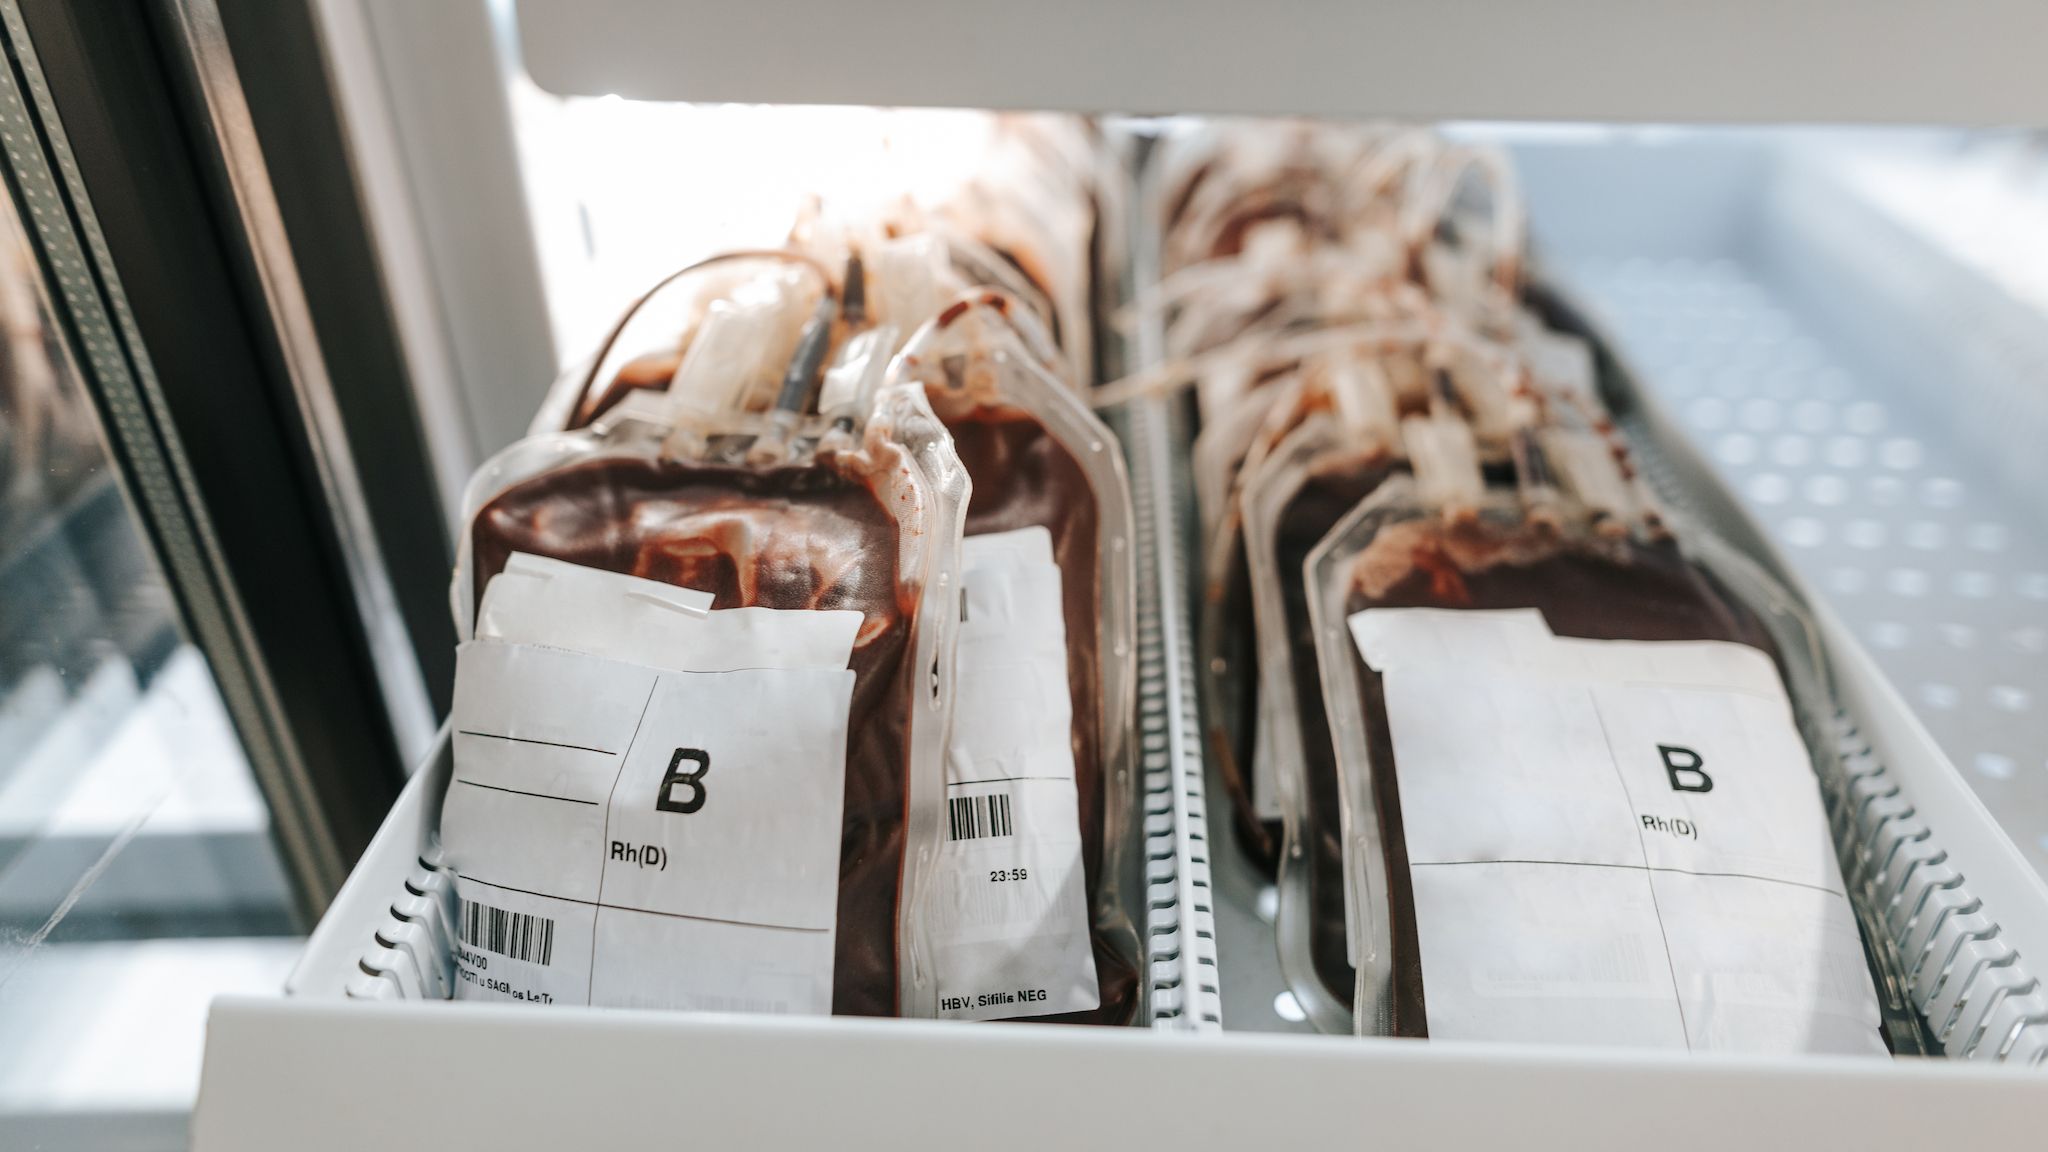
Many news outlets claim to have seen materials — namely, in now-deleted Telegram posts — in which Russia-aligned hacking groups Noname057(16) and Z-Pentest are claiming responsibility for the attacks. Z-Pentest reportedly posted 2,500 lines of Danfoss code, but none of these alleged materials have been published. The purported hackers claim the attacks are about highlighting bad cybersecurity practices.
It's tempting to once again bring up AI agents as vehicles of cyber-destruction, but the reality is that, just like what happened with PHP , most of the time all bots are actually doing is revealing shoddy security practices and/or copious amounts of technological debt.
Follow Tom's Hardware on Google News , or add us as a preferred source , to get our latest news, analysis, & reviews in your feeds.
Bruno Ferreira Social Links Navigation Contributor Bruno Ferreira is a contributing writer for Tom's Hardware. He has decades of experience with PC hardware and assorted sundries, alongside a career as a developer. He's obsessed with detail and has a tendency to ramble on the topics he loves. When not doing that, he's usually playing games, or at live music shows and festivals.
hotaru251 are just to expose bad security no or you wouldnt cause damages (especially targeting blood which is finite and critical for some people to survive) if you WERE only about showing bad security you'd msg them about it and show them you can do stuff at a specific time on a non critical thing so they can see it happen but also fix issue before causes a larger issue. Reply
PEnns "Once again, the root cause is a lack of essential cybersecurity practices, rather than super-intelligent AI bots" Gaslighting was never so popular as these days. One could also say: "Once again, the root cause for extremely destructive cyber attacks are super-intelligent AI bots." Reply
alan.campbell99 hotaru251 said: no or you wouldnt cause damages (especially targeting blood which is finite and critical for some people to survive) if you WERE only about showing bad security you'd msg them about it and show them you can do stuff at a specific time on a non critical thing so they can see it happen but also fix issue before causes a larger issue. Aye, it takes a special breed of vermin to mess with anything critical that is health or hospital-adjacent. They can DIAF. Reply
DS426 France is almost like a modern-day fall of Rome… just without the giant sphere of influence that Rome had at the time, lol. Reply
Key considerations
- Investor positioning can change fast
- Volatility remains possible near catalysts
- Macro rates and liquidity can dominate flows
Reference reading
- https://www.tomshardware.com/tech-industry/cyber-security/SPONSORED_LINK_URL
- https://www.tomshardware.com/tech-industry/cyber-security/blood-banks-in-france-hit-by-temperature-raising-attacks-on-fridges-purported-hackers-claim-attacks-are-about-cybersecurity-not-malice#main
- https://www.tomshardware.com/membership
- Tesla unveils AI accelerator roadmap, adopts new 'SI' branding in 'Super Intelligence' push
- Combined OpenSSH and musl-libc flaws let anyone into Alpine Linux and other distros by typing anything over 256 characters as a password
- Thin, Light and Built for Everything: NVIDIA RTX Spark Windows Laptops Gain New Models, Agent Tools and Games
- Rogue AI tasked with renumbering pages accidentally deletes law professor's entire syllabus, one year of lecture notes
- Grab a huge 44% saving on a 4K 43-inch Samsung smart monitor, now under $280
Informational only. No financial advice. Do your own research.